
Cyber criminals are targeting business email accounts at an accelerated rate, particularly at organizations using cloud-based programs, says a new report from specialist insurer Beazley.
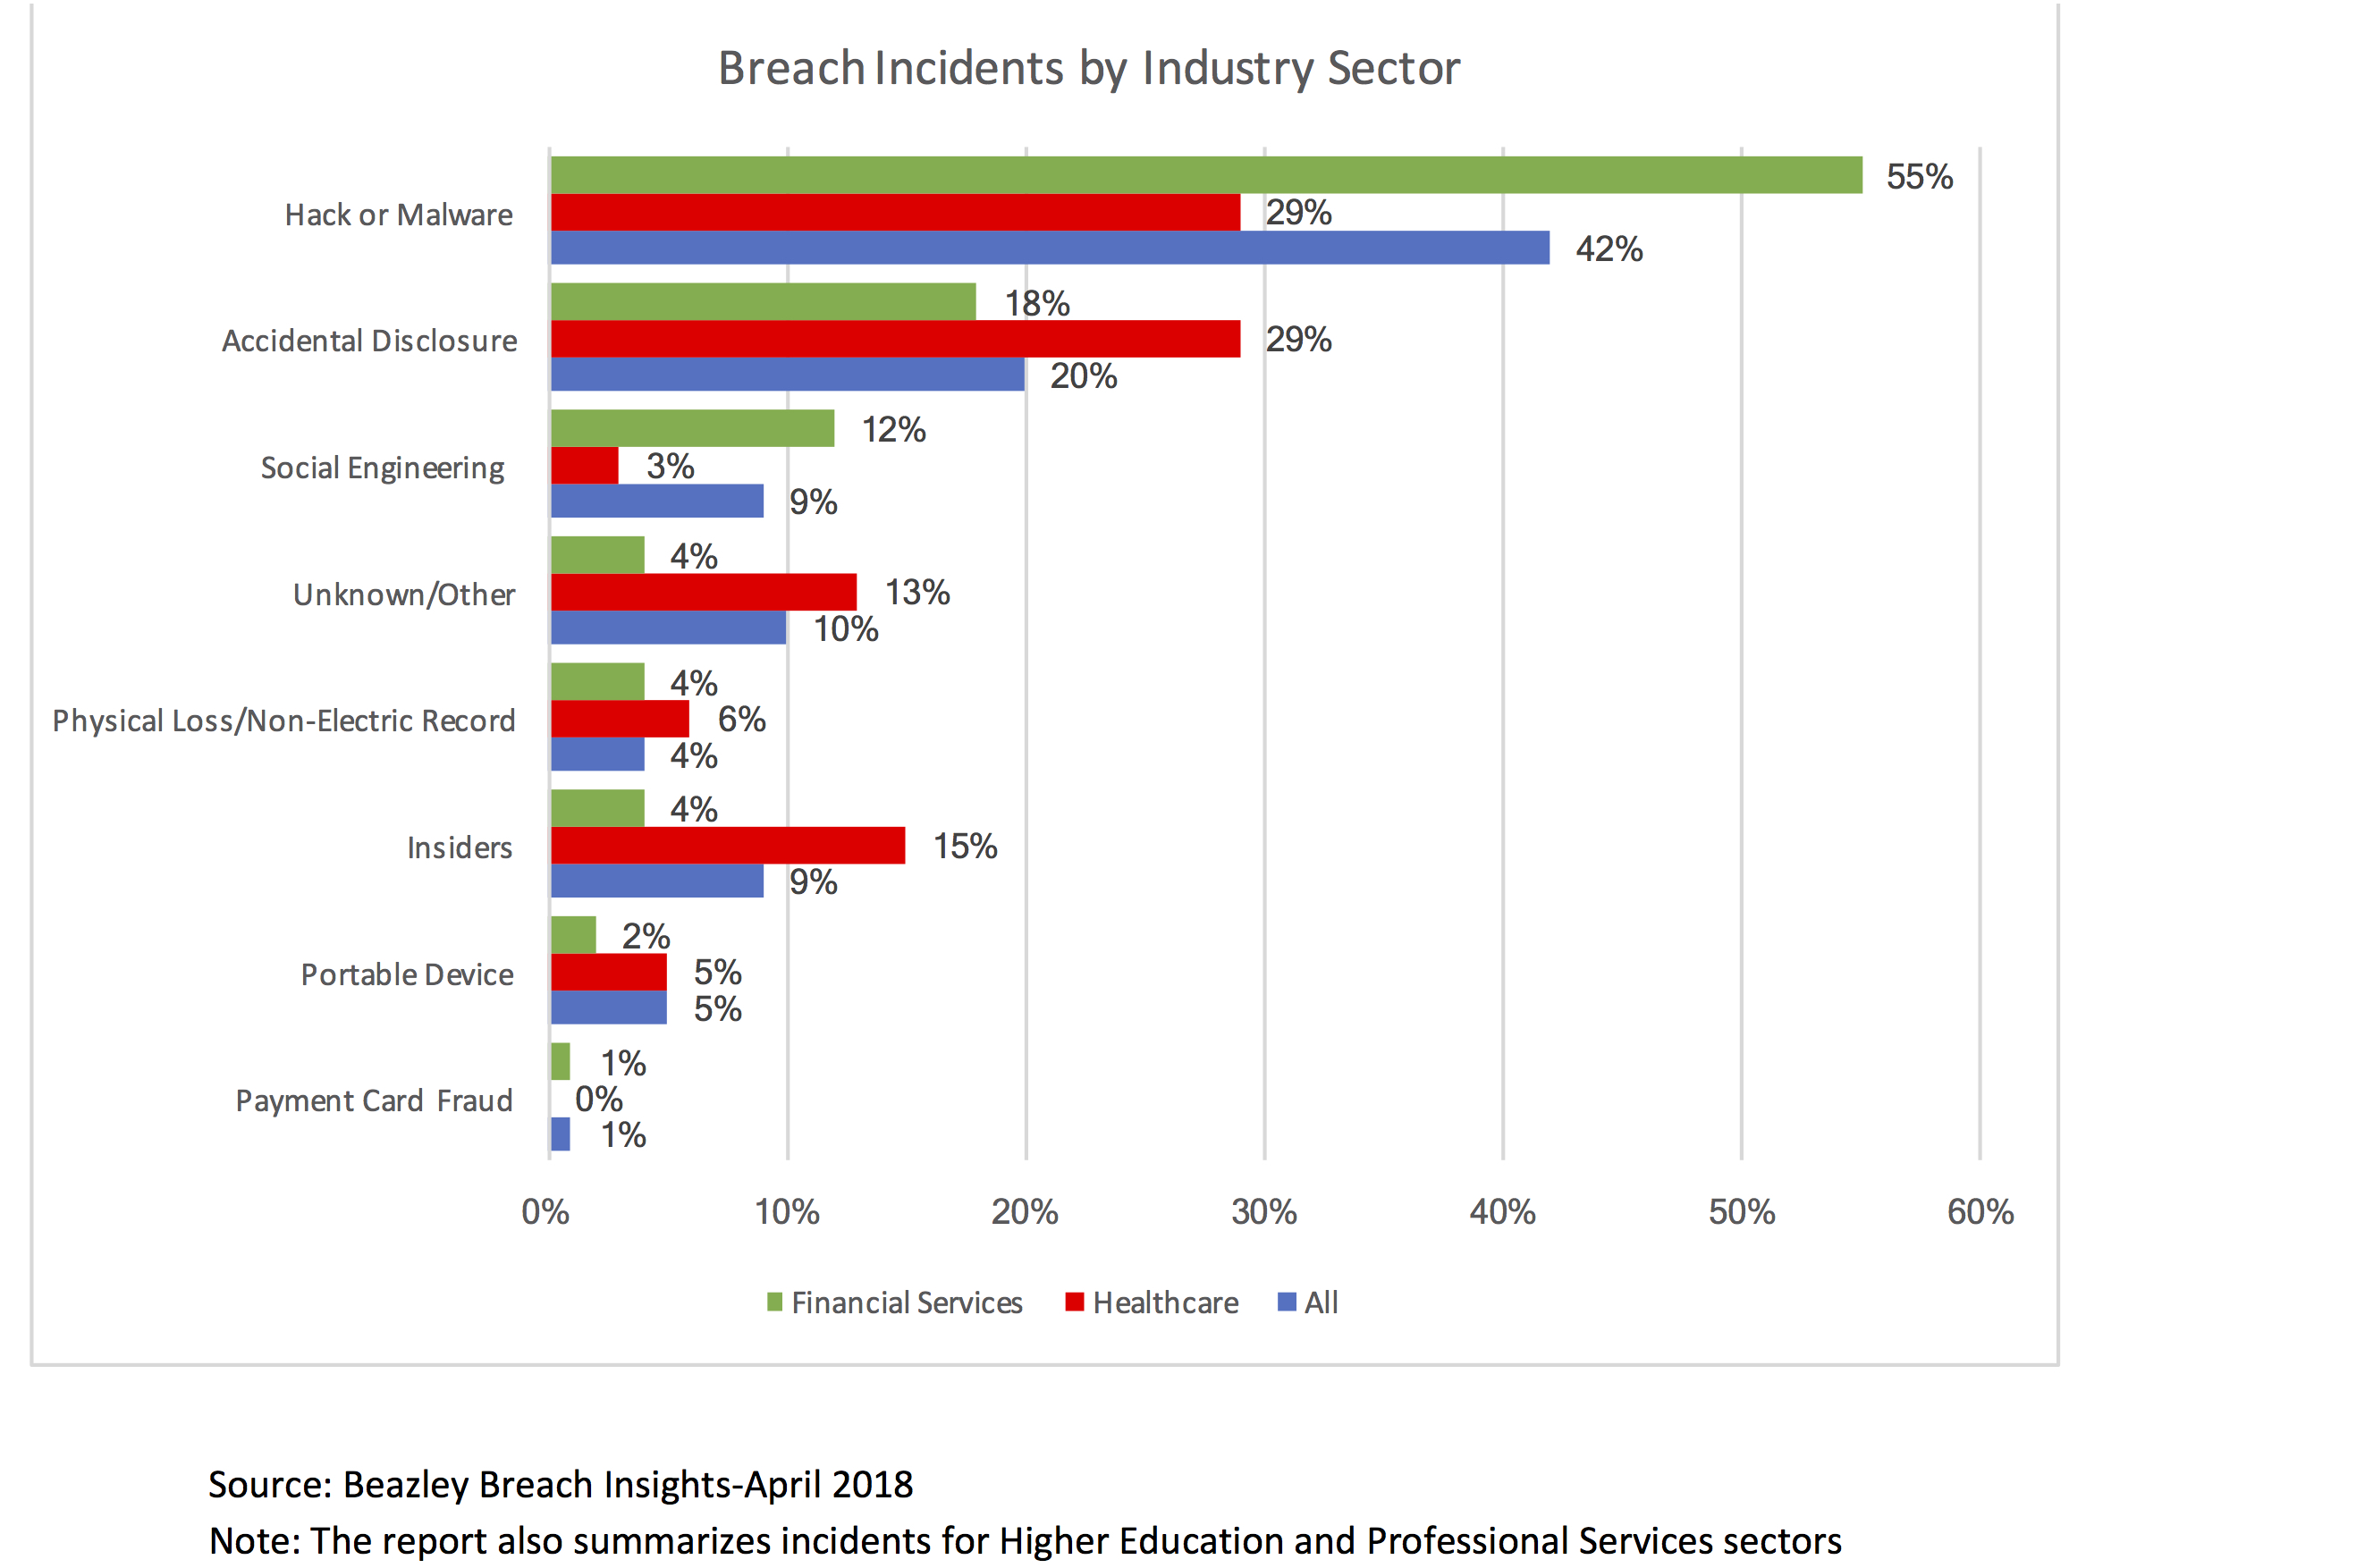
The top two causes of data breaches reported to the Beazley Breach Response (BBR) Services team during first-quarter 2018 were hack or malware (42 percent) and accidental disclosure (20 percent), according to the Beazley Breach Insights-April 2018 report. The three sectors most affected were financial services, healthcare and professional services.
Beazley said these hacking incidents usually occur when an employee clicks on a link in a phishing email, HelpDesk message or Microsoft survey. The employee is then redirected to a legitimate-looking website and asked for email credentials. This allows cyber criminals to log into the account undetected, where they can provide fraudulent instructions to divert and steal payments made by or to the organization, as well as access personally identifiable information.
If the organization uses a cloud-based program such as OneDrive, the cyber criminal will gain access to all files the employee can access, Beazley said.
The report recommended a number of tips organizations can use to protect themselves against these attacks, such as requiring two-factor authentication, enforcing strong password policies and training all employees to beware of phishing attempts.
 Viewpoint: What U.S. Insurers Should Learn From the EU AI Act
 Another Perspective: Shaking Hands and Teaching Trust at Reinsurance Broker Holborn
 Register: AI Tools for FNOL & Digital Claims Intake ‘Demo Day’ on September 16
 Federal Terrorism Insurance Backstop Prompted by 9/11 Still Waits for Reauthorization